

1/30/2016 Problem Restarting Apache2: Solutions
If you're using apache 2 as webserver maybe sometimes you'll have to deal with common problems like vhost, syntax errors, bad configurations. Sometimes is when you edit a file inside /etc/apache2/sites-enabled/file.conf and maybe your edition just didn't accomplish with the syntax so here is how can you check :
1. Make sure that your Apache2 service is up and running.
If this isn't the output, read carefully the error.
2. Check your systemctl status, this will give you a lot of information.
References:
[1]http://www.techrepublic.com/article/troubleshoot-apache-problems-with-these-tips/
[2]https://www.digitalocean.com/community/tutorials/how-to-troubleshoot-common-site-issues-on-a-linux-server
[3]https://www.linode.com/docs/troubleshooting/troubleshooting-common-apache-issues
1. Make sure that your Apache2 service is up and running.
user@~$sudo service apache2 status
● apache2.service - LSB: Apache2 web server
   Loaded: loaded (/etc/init.d/apache2; bad; vendor preset: enabled)
   Active: active (running) since Fri 2016-01-29 14:05:16 EST; 14s ago
     Docs: man:systemd-sysv-generator(8)
  Process: 31573 ExecStop=/etc/init.d/apache2 stop (code=exited, status=0/SUCCESS)
  Process: 17063 ExecReload=/etc/init.d/apache2 reload (code=exited, status=0/SUCCESS)
  Process: 30948 ExecStart=/etc/init.d/apache2 start (code=exited, status=0/SUCCESS)
  ...
If this isn't the output, read carefully the error.
2. Check your systemctl status, this will give you a lot of information.
user@~$sudo systemctl status apache2.service
● apache2.service - LSB: Apache2 web server
   Loaded: loaded (/etc/init.d/apache2; bad; vendor preset: enabled)
   Active: failed (Result: exit-code) since Fri 2016-01-29 13:48:57 EST; 18s ago
     Docs: man:systemd-sysv-generator(8)
  Process: 31573 ExecStop=/etc/init.d/apache2 stop (code=exited, status=0/SUCCESS)
  Process: 17063 ExecReload=/etc/init.d/apache2 reload (code=exited, status=0/SUCCESS)
  Process: 30467 ExecStart=/etc/init.d/apache2 start (code=exited, status=1/FAILURE)
3. Run the apache config test. It is always a good idea to run configtest everytime you make changes to the apache2 config file so that you won't accidentally stop apache2 service user@~$ sudo apache2ctl configtest AH00558: apache2: Could not reliably determine the server's fully qualified domain name, using 127.0.1.1. Set the 'ServerName' directive globally to suppress this message Syntax OK4. Restart the apache service
user@~$ sudo service apache2 stop && sudo service apache2 start
References:
[1]http://www.techrepublic.com/article/troubleshoot-apache-problems-with-these-tips/
[2]https://www.digitalocean.com/community/tutorials/how-to-troubleshoot-common-site-issues-on-a-linux-server
[3]https://www.linode.com/docs/troubleshooting/troubleshooting-common-apache-issues
1/29/2016 Video Writeup EFF-CTF 2016
For a while I've been trying to understand a little bit about reversing and low level stuff, sometimes it becomes a little difficult but if you want you can, so this post it is to highlight a youtube channel that I've been checking in this vacations it the Liveoverflow's great videos that solves a few reversing challenges. As you know the most recent security conference was the Usenix enigma as it's commonly in this kind of Cons there was a Capture The Flag , The EFF was runing a hacking contest at Enigma! The challenges included web hacking, binary analysis, cryptography challenges, and
more.
So LiveOverflow solve this after a few hours and he posted this on his youtube channel, so here it is .
So LiveOverflow solve this after a few hours and he posted this on his youtube channel, so here it is .
1/28/2016 NSA’s top hacking boss explains how to protect your network from his attack squads

True words have not been spoken at the Usenix enigma conference it seems that the Nsa's top hacking boss is explaining how they exploit your networks and he is giving free advices... I doubt it, I've seen a lot of systems over the time and wherever I've been, security invariably sucks even in the places where they really know it does suck. So, it's not a non sequitir to state that they'd probably be more secure with someone else handling the data at rest part of the equation or data in transit within the cloud provider.
Data in transit and data at rest still on premises will remain key
determiners of exactly how the overall security posture rates up or
rates down. A proper provider will help the business to lock down the in
transit data as well. Then only the on premises setup will be the only
part that sucks.Security is a process and the number of people that actually can read
and apply proper processes is vanishingly small if it's possible, to
advance your systems security and understand it just do it, and the first step is to encrypt everything, and trying to mitigate adding more layers of security.
I respect all people working in US goverment but as you know according to the recent statistics of some resources [Check spiegel.de] say that USA is the largest invading privacy , because they don't respect the American rights over national security , also we know that MI6 and other intel agencies are reading alien code searching for explotaible bugs. This is a game where the number one player is USA , and that talk given by Roy Joice is strange because he is part of that exploiters team.
I respect all people working in US goverment but as you know according to the recent statistics of some resources [Check spiegel.de] say that USA is the largest invading privacy , because they don't respect the American rights over national security , also we know that MI6 and other intel agencies are reading alien code searching for explotaible bugs. This is a game where the number one player is USA , and that talk given by Roy Joice is strange because he is part of that exploiters team.
1/21/2016 What is Practice?
- Practice is a habit.
Practice is a routine.
Practice does not need to remember.
Practice comes by practicing.
Practice needs dedication and commitment. - To become a successful devops-pentester you need lot of practice, dedication and commitment
1/16/2016 The Traveling Salesman Problem
This week when I was reading about Brute Force password attacks in a Ukranian Course that I'm taking I just see how a cool implementation done by Dr Michel Wermelinger's seems pretty cool and easy explanation about how you can achieve all the nodes, just click on the image below to interact.

12/30/2015 The Origin of the Cyber-War:China

If you've ever heard about cyberwar, and the big players of this like China, Russia, USA, among others, I found an interesting article checking my timeline of twitter in which a Chinese blog tells how China has been in this field, remember that source is written by someone that we don't know, so you're the final analist.
The Article consists of three parts:

Hope you enjoy the reading, and happy new year to every reader of the blog.
c1b3r.
12/05/2015 Open Science for my Article of Communications Techniques Class at UTP
Maybe one of the most important thing in the world is how we talk to each other, it seems that sometimes there are communications barriers and develop and improve an effective communication toolset(skills in the end) can't be done inside a class, you need to put in practice some tips, tricks given in the classroom outside of it, because your body is always communicating.
So this blog post is not going to be about computer security or relate it, it's my invitation to you to read and article written by me and my fellow Sebastian Zapata this was and assignment in the communication techniques class meet the following requirements :
- Read and use the arguments of the textbook 'Redacción Técnica '
- Write an article based on the image below, and release the article under Open Science movement [1]
- Use the American Psychological Association rules.
 |
| Fig.2 scientific method, Spanish Version. |
So here is a short summary of our work done :
 |
| Fig.2 Work done, Ascendent order |
You will find this article in tex and pdf format in the next link :
Articulo de Técnicas Comunicación [Full Text in Spanish]
See you next
[1] https://en.wikipedia.org/wiki/Open_science: Open science is the movement to make scientific research, data and dissemination accessible to all levels of an inquiring society, amateur or professional. It encompasses practices such as publishing open research, campaigning for open access, encouraging scientists to practice open notebook science, and generally making it easier to publish and communicate scientific knowledge
I stopped working with the professor of electrical technology for this.
UPDATE:
Due to this research , I've had problems with some professors and teachers they claim that I'm evil and a destroyer for reveal potential risks to the public, meanwhile I don't think about this as a problem because it exist inside the campus and that's happening in other national campus around Colombia, This shows how bad prepared are the professionals who manages network of the university, without generalizing of course.
I stopped working with the professor of electrical technology for this.
11/30/2015 Programming Contest
Programming Contest are not very different to Capture the Flag, as you know a CTF is a special kind of information security competitions where categories can be Web, Forensics, Crypto, Binary, or something else, The main Idea is solve challenges, meanwhile Programming Contest is the same but here I can notice clearly an academic approach which includes mathematics , physics, statistics, data structures, and other topics that maybe I don't know yet, This entrance is to express How I feel in my first Programming Contest sponsored by RPC (Red de Programación Competitiva).
As always I was late at the event, starting at 1 p.m of 28 day of November, Universidad Tecnológica de Pereira was the host of this competition, the idea of me participating in this contest was to know more about how it is,What kind of problems I need to face in the future, and the most important if it's funny because if you don't like this just quit out.
My team was conformed by two more people Leiver a fellow class of the operations research and a new friend that certainly looked pretty smart Sebastian, both of them have a lot of experience in this kind of competitions, is obviously that a team is a conformation to speak also It was to generate synergy, new ideas, discuss problems, and share knowledge in how to solve this or that problem, but that did not happen here apparently I do not know many issues, nor have methods in mind I just could think myself in the problems and maybe share my thoughts, because that was the only thing that happened. To me this experiment was interesting because I'm confident with myself that I need to learn much more, and increase my expertise in Computer programming, of course there is a goal behind this,and it needs to be part of my personal toolkit as a hacker.
Things that I learn :
If you're going to use c++ you can use this trick,
And It simply optimize cin and cout by making its execution faster, using a kind of syncronization; Off course participants in this competition like in the Ctf's Wargames, need to practice, practice, and practice to get a decent standard math and programming level, here we need to know what type of problem is, and based on that we can use one or other method, something funny to me was when the competition runs out of time everybody was talking about a DP, P,Complexity,Graphs, that was blowing my mind...Something new in this short weekend.
Stay tune !
Reference:
[1]Codeforces
[2]Competitive Programming
[3]Key Advantage of Competitive Programming
[4]PicoCTF: A Game-Based Computer Security Competitionfor High School Students
[1]Developing Small Team-based Cyber SecurityExercises
As always I was late at the event, starting at 1 p.m of 28 day of November, Universidad Tecnológica de Pereira was the host of this competition, the idea of me participating in this contest was to know more about how it is,What kind of problems I need to face in the future, and the most important if it's funny because if you don't like this just quit out.
My team was conformed by two more people Leiver a fellow class of the operations research and a new friend that certainly looked pretty smart Sebastian, both of them have a lot of experience in this kind of competitions, is obviously that a team is a conformation to speak also It was to generate synergy, new ideas, discuss problems, and share knowledge in how to solve this or that problem, but that did not happen here apparently I do not know many issues, nor have methods in mind I just could think myself in the problems and maybe share my thoughts, because that was the only thing that happened. To me this experiment was interesting because I'm confident with myself that I need to learn much more, and increase my expertise in Computer programming, of course there is a goal behind this,and it needs to be part of my personal toolkit as a hacker.
Things that I learn :
If you're going to use c++ you can use this trick,
#include <bits/stdc++.h>There is no need to include any other header files here and it's interesting because in stack overflow there is a question related to this :
How does #include <bits/stdc++.h> work in C++?:
It is basically a header file that also includes every standard library and stl include file. The only purpose I can see for it would be for testing and education, please refer to https://gist.github.com/eduarc/6022859 to see an example, I don't exactly know if it's true that this increase the compilation timetrick that didn't make sense to me was use:
#define fast ios_base::sync_with_stdio(false);cin.tie(NULL)
And It simply optimize cin and cout by making its execution faster, using a kind of syncronization; Off course participants in this competition like in the Ctf's Wargames, need to practice, practice, and practice to get a decent standard math and programming level, here we need to know what type of problem is, and based on that we can use one or other method, something funny to me was when the competition runs out of time everybody was talking about a DP, P,Complexity,Graphs, that was blowing my mind...Something new in this short weekend.
Stay tune !
Reference:
[1]Codeforces
[2]Competitive Programming
[3]Key Advantage of Competitive Programming
[4]PicoCTF: A Game-Based Computer Security Competitionfor High School Students
[1]Developing Small Team-based Cyber SecurityExercises
11/28/2015 Linux Kernel, Security or Myth?

Recently I was reading an interesting interview who Craig Timberg made to Torvalds. Clearly the principal argument in the interview is the increase of known vulnerabilities in the linux Kernel and obviously the mindset of the lead developer of Linux, who is arguing that security is another concern more.
Even more broadly, the battle over Linux security is a fight over the future of the online world. At a time when leading computer scientists are debating whether the Internet is so broken that it needs to be replaced, the network is expanding faster than ever, layering flaw upon flaw in an ever-expanding web of insecurity. Perhaps the best hope for fixing this, some experts argue, lies in changing the operating system that — more than any other — controls these machines.
Kernel Security is pretty important right now and if you don't believe in that check the statistics in android's phone usage, also you can take a quick Look at a few recent kernel security holes that has been discovered Buffer Overflows, initialization failures and the list goes on. The point is that been Torvalds the king of geeks he is obviously going to be the king of the bad guys if they don't review properly commits and new patches, security is above usability or I think so, that's why Security of Linux even as it became a bigger is more important, but seriously Torvalds just said that People in security is just too paranoid.I remember when long time ago Linux in its early days was widely considered a safer choice than Windows or other commercial operating systems, but now it has been disappear slowly. I have to say that not all problems did not involve the kernel itself, but they're there, and it's becoming a popular target for hackers building “botnets,” and the companies that sell them surveillance tools like Finfisher.
Could be The Kernel Security taking as a relevant topic ?
References:
[1] http://www.washingtonpost.com/sf/business/2015/11/05/net-of-insecurity-the-kernel-of-the-argument/
[2] https://lwn.net/Articles/661086/
[3] https://lwn.net/Articles/662627/
[4] http://bits-please.blogspot.com.co/2015/08/android-linux-kernel-privilege.html
[5] https://lwn.net/Articles/662219/
[1] http://www.washingtonpost.com/sf/business/2015/11/05/net-of-insecurity-the-kernel-of-the-argument/
[2] https://lwn.net/Articles/661086/
[3] https://lwn.net/Articles/662627/
[4] http://bits-please.blogspot.com.co/2015/08/android-linux-kernel-privilege.html
[5] https://lwn.net/Articles/662219/
5/18/2015 Before you learn to code, think about what you want to code...
Checking Quora I found an answer pointing out to this nice article [1], so I would like to keep this in mind.
Cecilly Carver
[1] https://medium.com/@cecilycarver/things-i-wish-someone-had-told-me-when-i-was-learning-how-to-code-565fc9dcb329
Knowing how to code is mostly about building things, and the path is a lot clearer when you have a sense of the end goal. If your goal is “learn to code,” without a clear idea of the kinds of programs you will write and how they will make your life better, you will probably find it a frustrating exercise.
I’m a little ashamed to admit that part of my motivation for studying computer science was that I wanted to prove I was smart, and I wanted to be able to get Smart Person jobs. I also liked thinking about math and theory (this book blew my mind at an impressionable age) and the program was a good fit. It wasn’t enough to sustain me for long, though, until I found ways to connect technology to the things I really loved, like music and literature.
So, what do you want to code? Websites? Games? iPhone apps? A startup that makes you rich? Interactive art? Do you want to be able to impress your boss or automate a tedious task so you can spend more time looking at otter pictures? Perhaps you simply want to be more employable, add a buzzword to your resume, or fulfill the requirements of your educational program. All of these are worthy goals. Make sure you know which one is yours, and study accordingly.
Cecilly Carver
[1] https://medium.com/@cecilycarver/things-i-wish-someone-had-told-me-when-i-was-learning-how-to-code-565fc9dcb329
5/04/2015 Filters with the IPV4 Address Space Assignment to .CO
It has been a long time since I wrote my last blog post, Just a little busy with the job and my university but this last weekend I was having a rest time, meanwhile I's reading about Ipv6 addressing tips for ISP's [1] I was wondering why I didn't play with the Lacnic assignments in the past, sometimes you just learn how internet in general works and you can go more deeper than it is.The Ipv4 assignments could be used to scan and check for new vulnerabities[2][3] inside a specific area or territory of the world.
Trying to get more information about Colombian's ip assignments we know that internet is a big number of connections between different AS, ASs are generally Internet service providers but can also be large companies, universities, and other such organizations who act as independent entities on the Internet. These AS's are responsible for assigning individual IP addresses and routing traffic from individual machines out to and in from the wider Internet, So we want to get more information about the Ipv4 assignments and the best way to get this is going to the primary source for IP address data and it's the regional Internet registries which allocate and distribute IP addresses through organizations located in their respective service regions, This regions are:
- African Network Information Centre (AfriNIC)
- American Registry for Internet Numbers(ARIN)
- Asia-Pacific Network Information Centre (APNIC)
- Latin American and Caribbean Internet Address Registry (LACNIC)
- RIPE Network Coordination Centre (RIPE NCC)

According to wikipedia the main aims are to :
Every Regional Internet registry has it's own ftp service sharing information related to the assignments [5] and also a mirror of the other RI'r.
- Protect the unallocated IP number resource pool,
- Promote and protect the bottom-up policy development process of the Internet, and
- Act as a focal point for Internet community input into the RIf system.
As it's shown in the picture you can see all the content inside the /pub (public folder)
 |
| Checking all the directory structure, assignments are in /pub/stats/region |
In my case I'm interest in all the IP addressing assignments by Lacnic and specifically my country Colombia.
Just get delegated-lacnic-extended-latest and delegated-lacnic-extended-latest.md5 files wich are that contains all the information That we need to play with, also notice the update history and the date in the ftp. |
| Getting files to play with |

cat delegated-lacnic-extended-latest|cut -d '|' -f  2|sort |uniq >country
cat country
Grepping by Country:
Now to get the information in what we're interests we need to filter our file by country and IPv4 the file itself has a 8 column format as is explained above:
Column 1:Regional Internet registry (Lacnic in this case)
Column 2:Country Code (CO)
Column 3:Ip Class,Type Resource (ASN,IPV4,IPV6)
Column 4:Network Begin
Column 5:Ip Address Quantity
Column 6:Assignment Date.
Column 7:Organization Type
Column 8: unknow for me.
cat delegated-lacnic-extended-latest | grep -i "CO|IPV4"and after that we get something like this :
lacnic|CO|ipv4|66.231.64.0|4096|19870101|allocated|75710
lacnic|CO|ipv4|131.0.136.0|1024|20140711|allocated|220116
lacnic|CO|ipv4|131.0.168.0|1024|20140714|allocated|218493
lacnic|CO|ipv4|131.108.168.0|1024|20140902|allocated|30093
We can get 375 entries but how many ipv4 addresses are assigned to CO in total?
off course this could be done filtering the 5 column and the IP to ASN Mapping Project
Team Cymru provides a number of query interfaces that allow for the mapping of IP addresses to BGP prefixes and Autonomous System Numbers (ASNs), based on BGP feeds from our 50+ BGP peers, and updated every 4 hours. This data is available through traditional WHOIS (TCP 43), DNS (UDP 53), HTTP (TCP 80), and HTTPS (TCP 443). For more information on the data available, and how to query, check out our IP to ASN Mapping Project.dding line per line in order to get the total number.
cat Colombia.txt |cut -d '|' -f5 |awk '{s+=$1} END {printf "%.0f", s}'
17.263.593 in IPv4 assignments to Colombian Country until the last update of file.In this amount of IPv4 Addresses we will be pretty interest in entities that don't waste time and money searching for you generally this type of entities are non-goverment such as universities, public schools but always without goverment asociation.Offcourse we can use a service to query for some basic AS information directly and for this I'm going to use the Team Cymru's nslookup.
The IP to ASN Mapping Project
Team Cymru provides a number of query interfaces that allow for the mapping of IP addresses to BGP prefixes and Autonomous System Numbers (ASNs), based on BGP feeds from our 50+ BGP peers, and updated every 4 hours. This data is available through traditional WHOIS (TCP 43), DNS (UDP 53), HTTP (TCP 80), and HTTPS (TCP 443). For more information on the data available, and how to query, check out our IP to ASN Mapping Project.Follow the steps given in the official website, using netcat is a better way to get this information, you can filter out the ips addresses using the next :
grep -i 'ipv4\|ipv6' Colombia.txt|cut -d '|' -f4 >ipsColombia.txtMaybe the previous won't work because you need to map an IPv6 address or prefix to a corresponding BGP Origin ASN.if you just want the ipv4 version :
grep -i 'ipv4' Colombia.txt|cut -d '|' -f4 >ipsColombia.txt
then add the begin and end word to the file.
netcat whois.cymru.com 43 < ipsColombia.txt | sort -n > asninfo.txt #ipv4, and ipv6

I hope that this information could be useful , cheers
c1b3rh4ck.
References
[1] http://portalipv6.lacnic.net/en/ipv6-addressing-tips-for-isps/
[2] http://www.sinfocol.org/2015/03/freak-on-colombian-domain-names-and-heartbleed-one-year-later/
[3] http://www.mcafee.com/us/resources/reviews/esg-vulnerability-manager.pdf
[4] http://cyber.law.harvard.edu/netmaps/methods.php
[5] ftp://ftp.lacnic.net/pub/stats
[6] http://www.team-cymru.org/IP-ASN-mapping.html
1/24/2015 What Happends When...
Checking the github feed I just found this nice link that you should read if you want to be more concious when you press the enter button:
Enjoy it:
https://github.com/alex/what-happens-when
Enjoy it:
This repository is an attempt to answer the age old interview question "What happens when you type google.com into your browser's address box and press enter?"
https://github.com/alex/what-happens-when
1/02/2015 Notes about Cyber Attacks
In this post I'd like to share with you some interesting notes that I've been collecting for a while, about cyberattacks and other cyber'put your word here lol' that we hear everyday in the news and maybe knowing that all the journalist and press in general are always doing mistakes in the usage of the words.
According to the book "Inside Cyber Warfare" This is an increasing field that has been taken as part of the patrimony of all nations.
There is a growing awareness of the vulnerability of a nation’s critical infrastructure to
network attack. Transportation, banking, telecommunications, and energy are among
the most vulnerable systems and may be subject to the following modes of attack:
• Insider threats
• Anonymous access to protected networks via the Internet and Supervisory Control
and Data Acquisition (SCADA)
• Counterfeit hardware
• Employee abuse of security guidelines leading to malware propagation inside the
firewall
So what would it happend if your country is under one cyber attack? What Would you do ?, here is something that you could do assuming that everything is connected (knowing that this is happening right now with the Internet of Things concept ).
Keep this things :
The History of Cyber Attacks Timeline:
Keep this things :
- A battery-powered radio capable of receiving NOAA alerts and two-way radios (walkie-talkies)
- solar-powered or hand-cranked radio as well
- Cash reserve should be kept within reach
- Social Security cards and other essential documents should also be held in a secure container,since access to a computer won’t be guaranteed
- Prepare a central point to speak with your family members take out power lines and cell phone towers
Online
safety tips
• Limit the amount of personal information you
post on social media sites, chat sites, forums and online games.
• Know and
use privacy settings provided on sites like Facebook and Twitter.
• Be
suspicious of unknown links or requests sent through email or text messages.
Don’t click on unknown links or answer strange questions sent to your mobile
device, regardless of who the sender appears to be.
• In your
email, turn off the option to automatically download attachments. Save and scan
any attachments before opening them.
• Verify
the authenticity of requests from companies or individuals by contacting them
directly, especially if you are being asked to provide personal information.
• Pay close
attention to website URLs. Malicious websites sometimes use a variation in
common spelling (petfun.com instead of petfun.net, for example) to deceive
unsuspecting computer users.
Links :
http://www.nato.int/docu/review/2013/cyber/timeline/EN/index.htm
Wikipedia's definition :
https://en.wikipedia.org/wiki/Cyber-attack
Norse's Map of Real time cyberattacks:
http://map.ipviking.com/
Wikipedia's definition :
https://en.wikipedia.org/wiki/Cyber-attack
Norse's Map of Real time cyberattacks:
http://map.ipviking.com/
12/21/2014 Sony 'made a mistake'???
The FBI filled in some blanks Friday by noting that "technical analysis of the data-deletion malware used in this attack revealed links to other malware that the FBI knows North Korean actors previously developed," including "similarities in specific lines of code, encryption algorithms, data deletion methods, and compromised networks." The FBI also found Internet addresses linked to North Korea in the malware involved in the attack
9/26/2014 #Shellshock Images of the Week
During these days we're hearing about #Shellshock bug, and I's just wondering if the Sysadmin of US DoD network is going to invite everybody to the big party with all these attacks,botnets, forkbombs,etc :P stay alert ,During all these two days one of the major flaws has been exploited and that's the obviously! , Who does not like free shells :3, there're right now tons of people creating new PoC's now imagine how money could you get :P Do you imagine how the defense should be.
I've been collecting a couple of fun pics regarding to this topic , enjoy it .
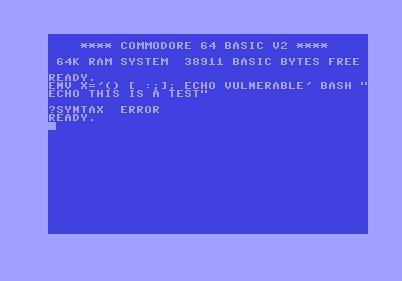
Fig.1 I can't reproduce #shellshock on this system either! Plz help.
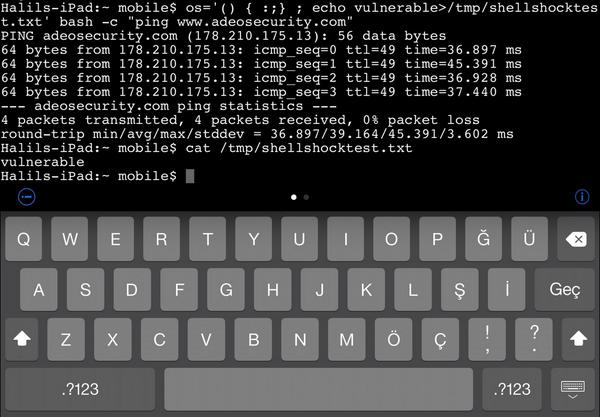
Fig.2 Jailbreaked iOS 7.1.2 #shellshock test result.
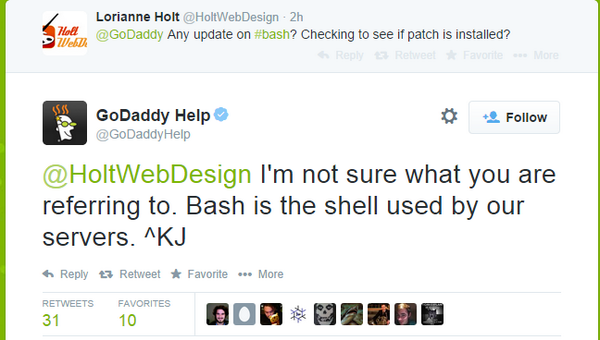
Fig.3 For a laugh: *Facepalm* Oh GoDaddy... #Shellshock #CVE20146271 #bashbug #bashbleed #bashpocalypse #infosec
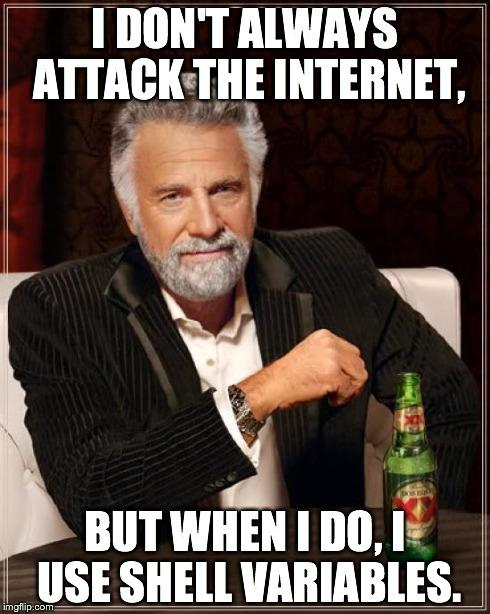
Fig.4 #infosec #shellshock #bashbleed #bashpocalypse
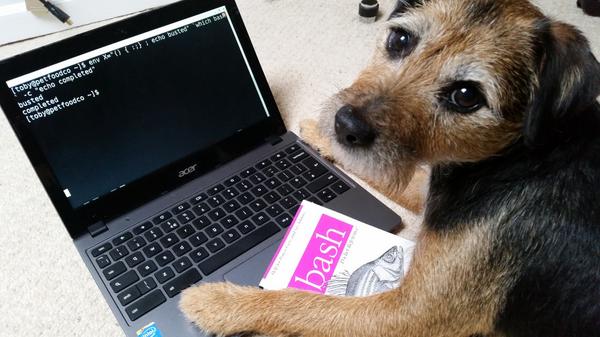
Fig.5 Lol In your servers, stealing your secretz #bashbug #shellshock
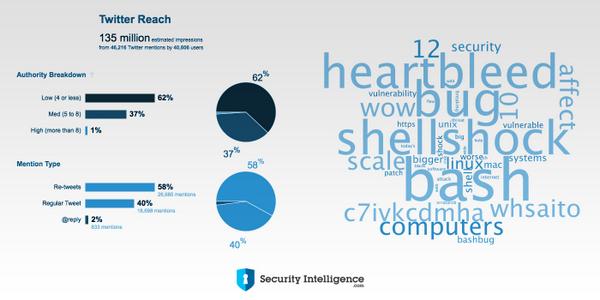
Fig.6 How many people already talking about #shellshock? About 40K tweets by 46K users since yesterday. #bash #bashbug

Fig.7 Since 90's ?
Fig.8 In the Wake of Shellshock, Mac Users Are Left Waiting for a Patch via @mashable http://avgclick.me/1n46EUP
#Shellshock: All you need to know about the #BashBug vulnerability http://symc.ly/1u21HMX
9/01/2014 Pwnables.kr

Well this post is to share with you an amazing site saw in #pwning channel ,I say that because in this site we can practice all the important aspects (Reversing, Programming, System Knowledge and Exploitation)it has a special thing where you need to know about Gnu/Linux Operative System and it is intended for students,professionals and enthusiast of Information Security.
The site is divided in four categories as it is explained below :
|
Play Just for fun not for profit.

4/20/2014 April 22nd is Earth day
This year I'm working with a near partner in my university as you maybe know in april 22 is Earth day an special day for our planet.We're going to plant new trees if you want to join please leave me a message using the contact box or reachme in twitter.

Plant trees plant life Pick a tree that you know can survive in your climate. If you're unsure about what that might be, ask an employee at your local garden shop, or inside the garden department of a big-box store.
Learn more about the environment. Earth Day is a good time to make a commitment to learning more about the environment and how you can help to protect it. Borrow some library books and read up on an issue such as pollution, endangered species, water shortages, recycling, and climate change. Or, learn about a region you've never considered before, like the Arctic, the deserts, or the rain forests. Think about the issues that concern you the most and if you haven't done so already, join a local group that undertakes activities to help protect the environment in your area.
Where:
Universidad Tecnologica de Pereira
When :
April 22 , at 9 a.m Electrical Building.
Subscribe to:
Posts (Atom)


